One record, from signature to shredder.
Custodyne is four connected parts: signed disposal approvals, tracked custody, sealed certificates, and the web app that holds it all together — each built so the record survives an audit. One intake and one signature can now cover a whole machine and every drive inside it.
Nothing moves without a signature
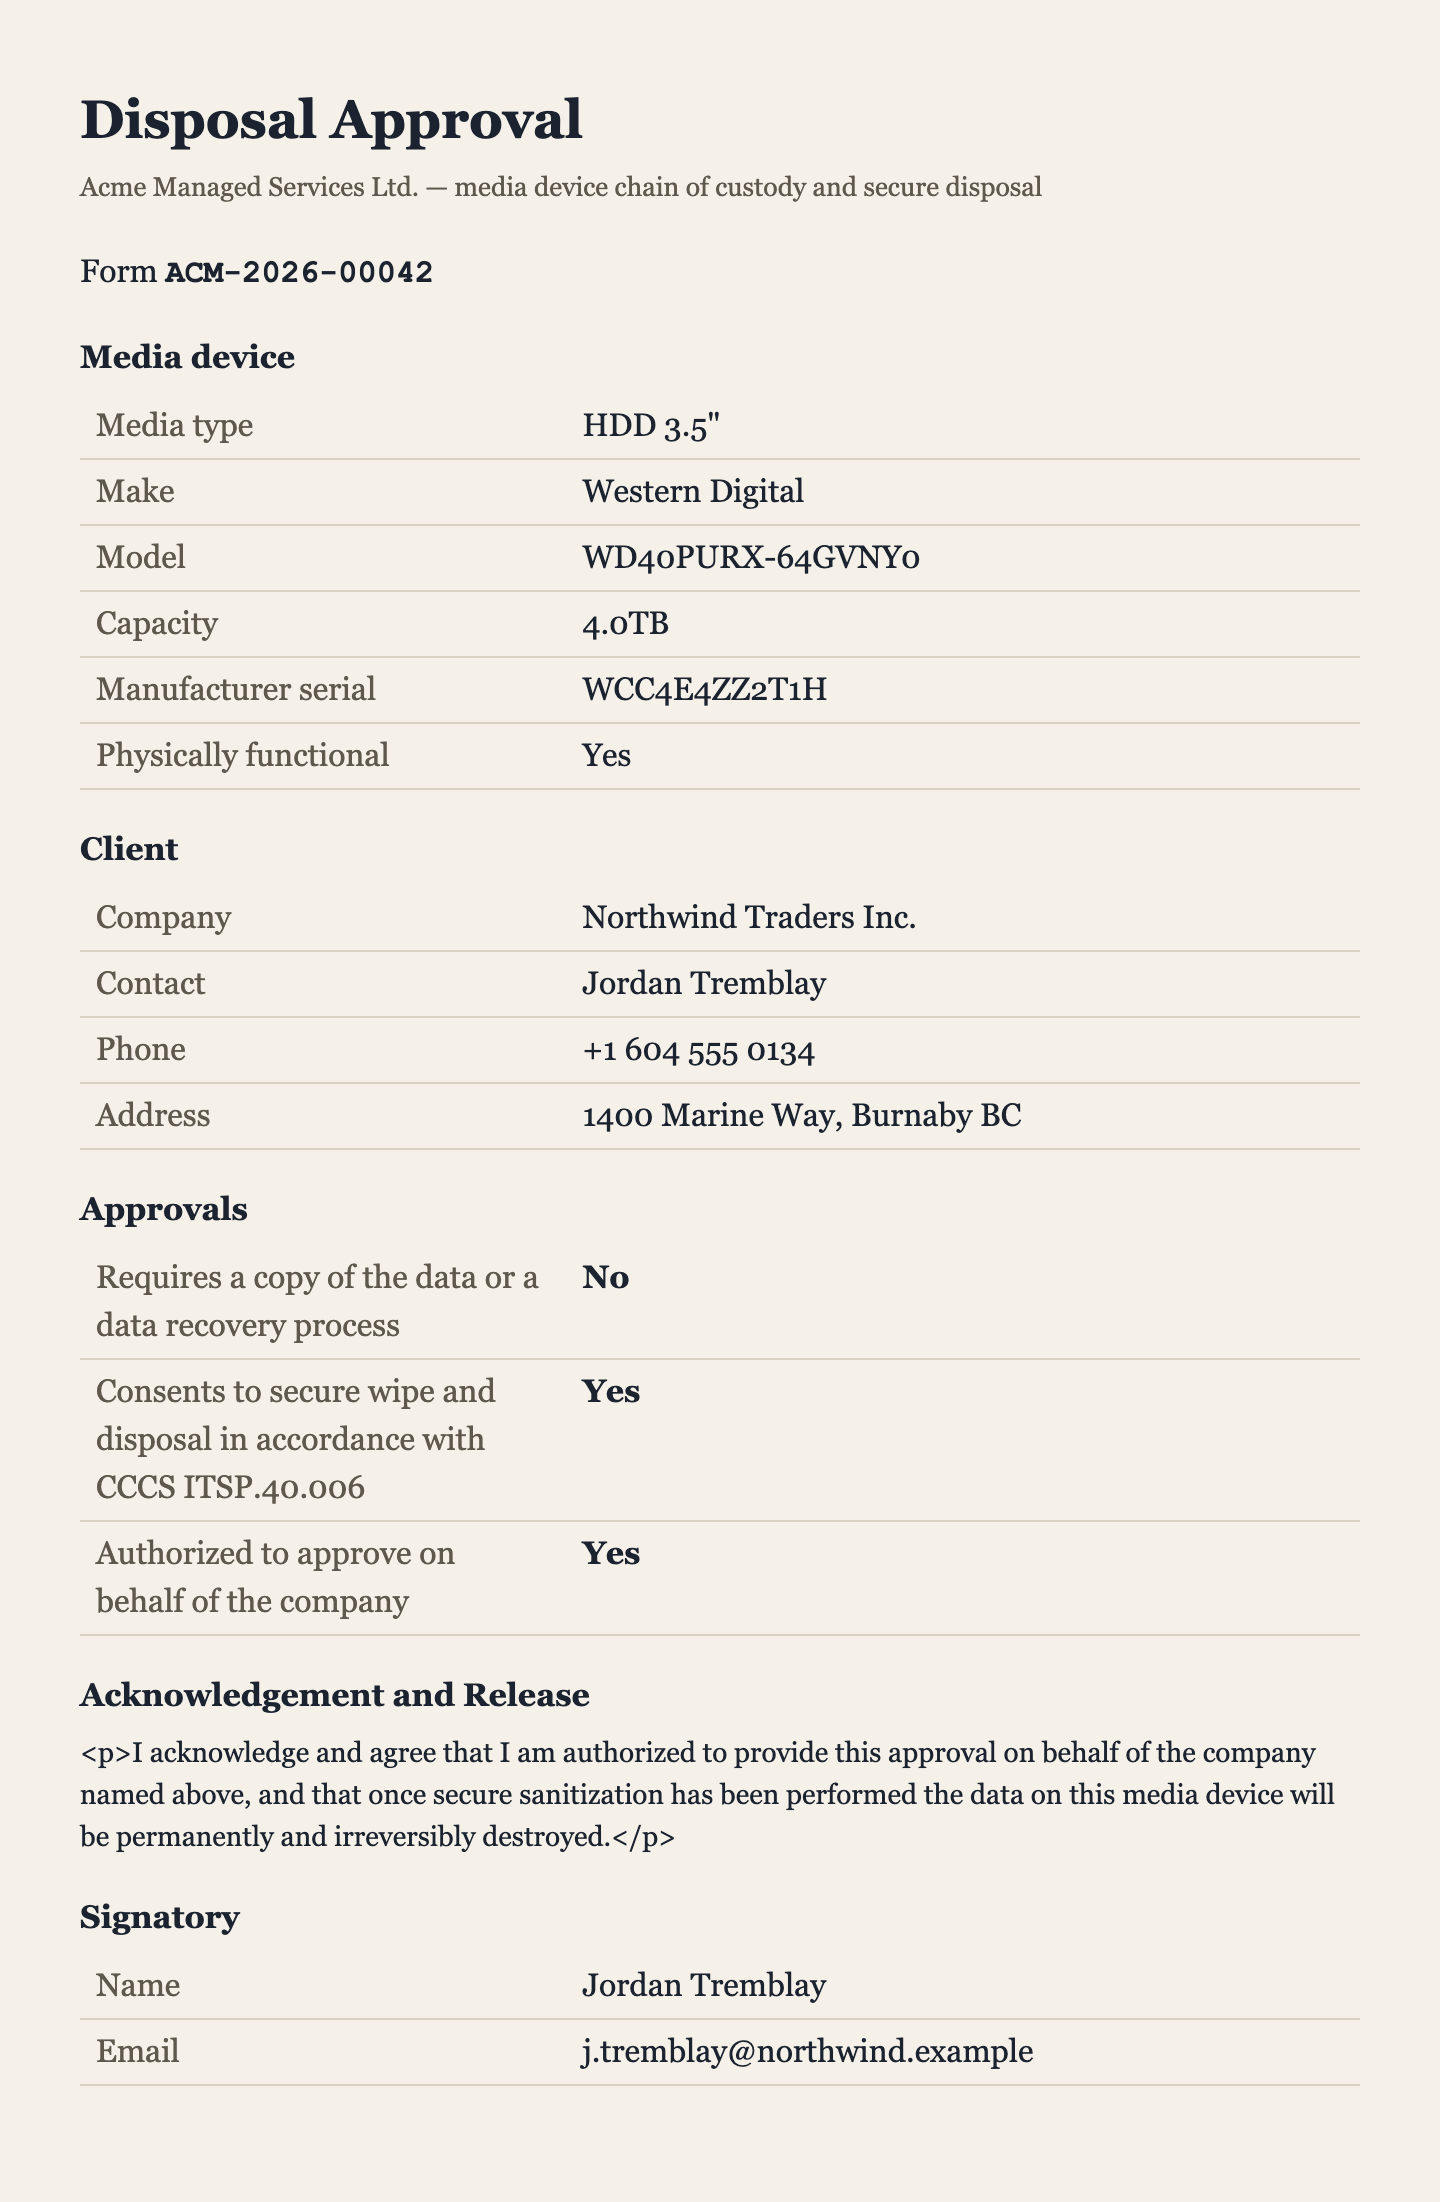
An electronic disposal approval names the media, the method, and the sanitization standard. The customer signs — on-device or by a single-use link — and the approval is bound to a SHA-256 hash of exactly what they saw.
ACM-2026-00042  LABEL PRINTED
ACM-2026-00042  INTAKE SCANNED
ACM-2026-00042  STAGED  BAY 3
ACM-2026-00042 HAND-OFF SIGNEDThermal labels and QR scans
Every drive and device gets a thermal label with a QR code, sized to your label stock — the layout adapts to the size you print. Pickup, transport, intake, and staging are each scanned, timestamped, and signed — an unbroken chain from possession to destruction.
Co-branded, hash-sealed proof
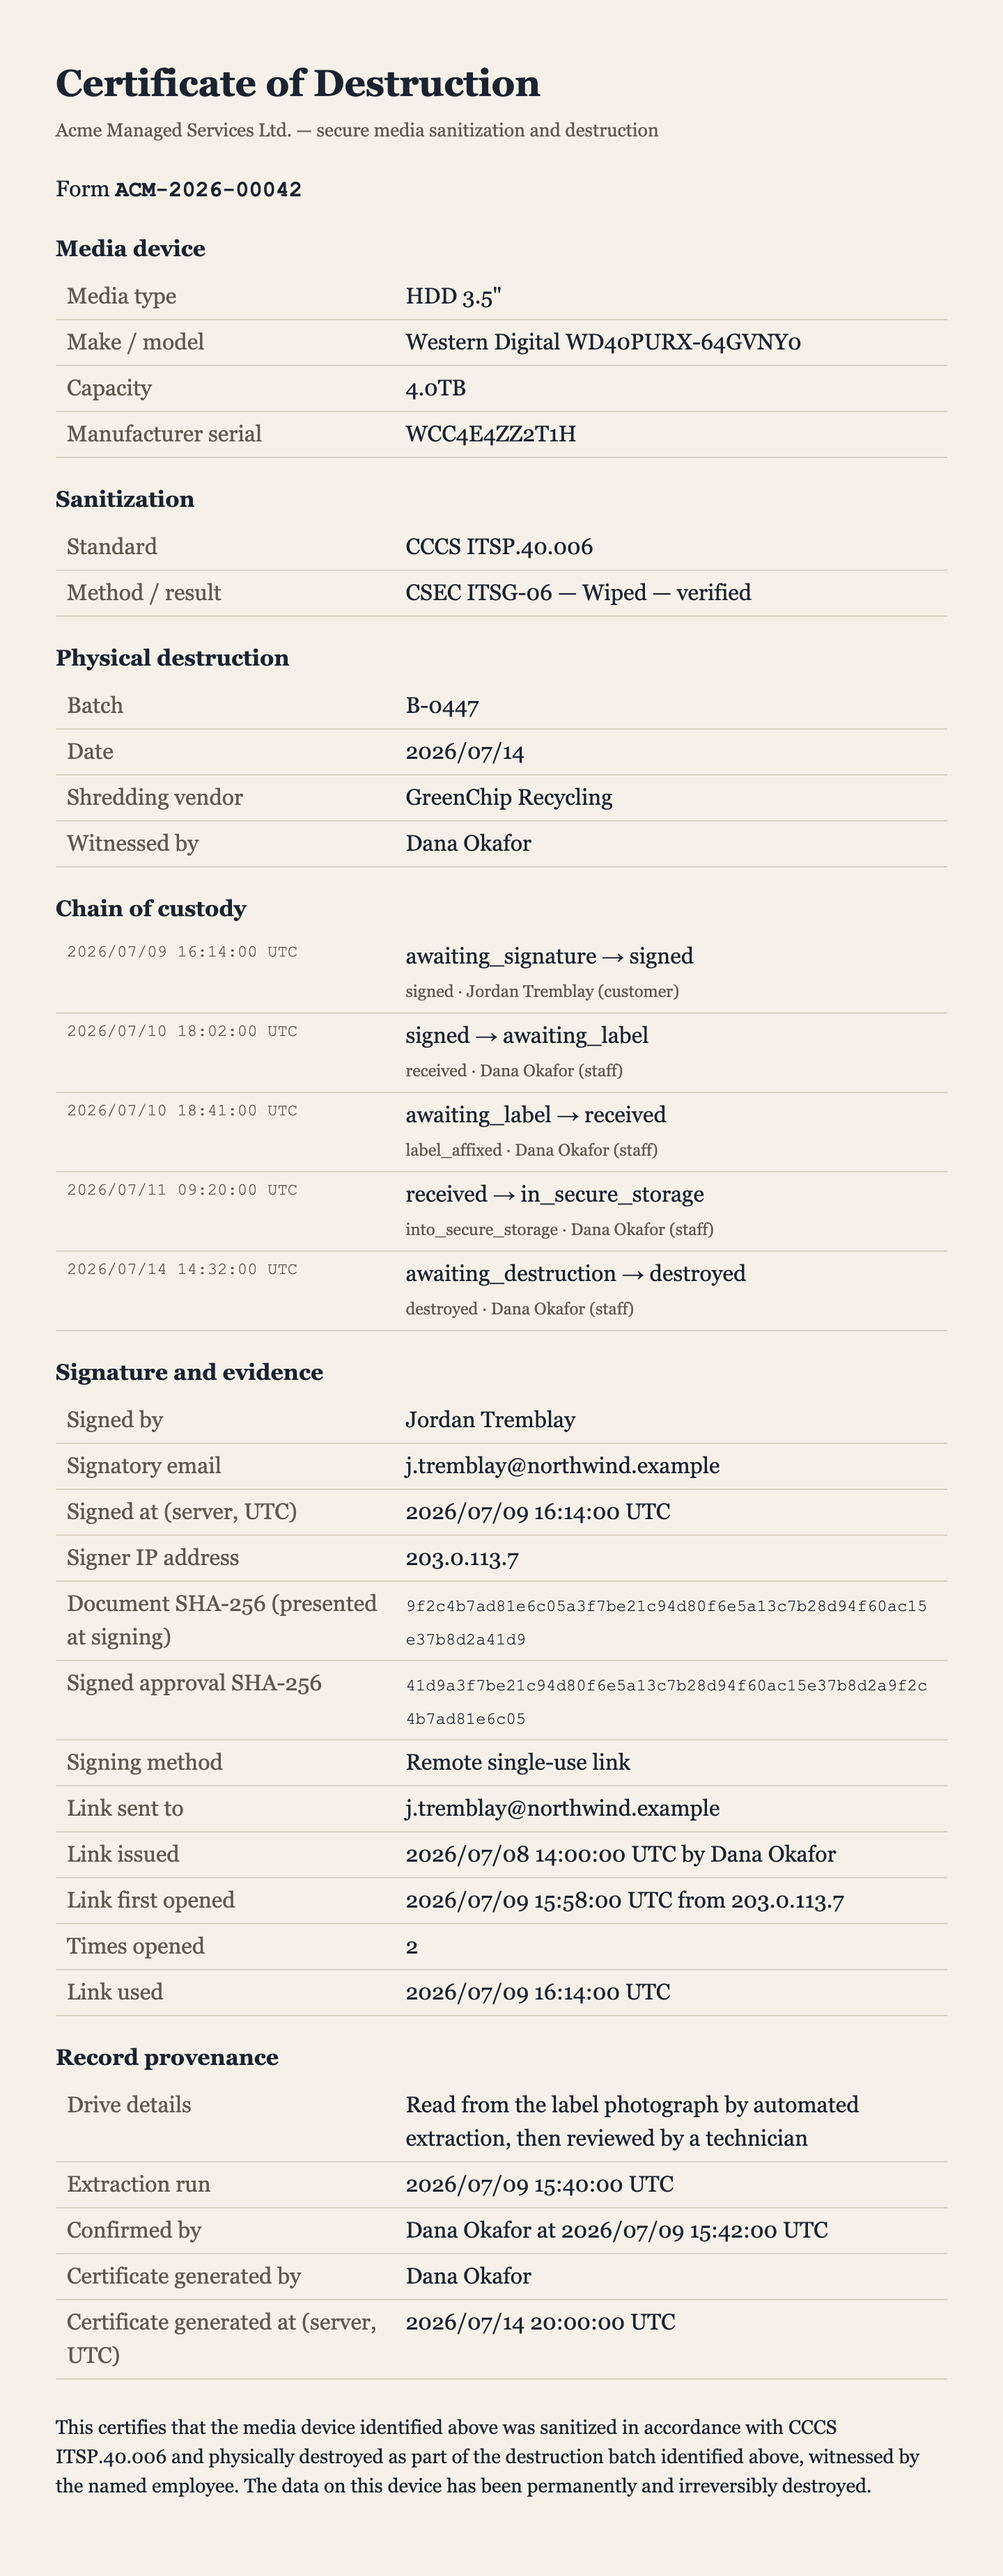
The Certificate of Destruction leads with your logo and cites the exact standard from the signed consent. A SHA-256 seal, a UTC timestamp, and a public verification URL make it independently checkable — any time.
Certify the machine, not just the drive
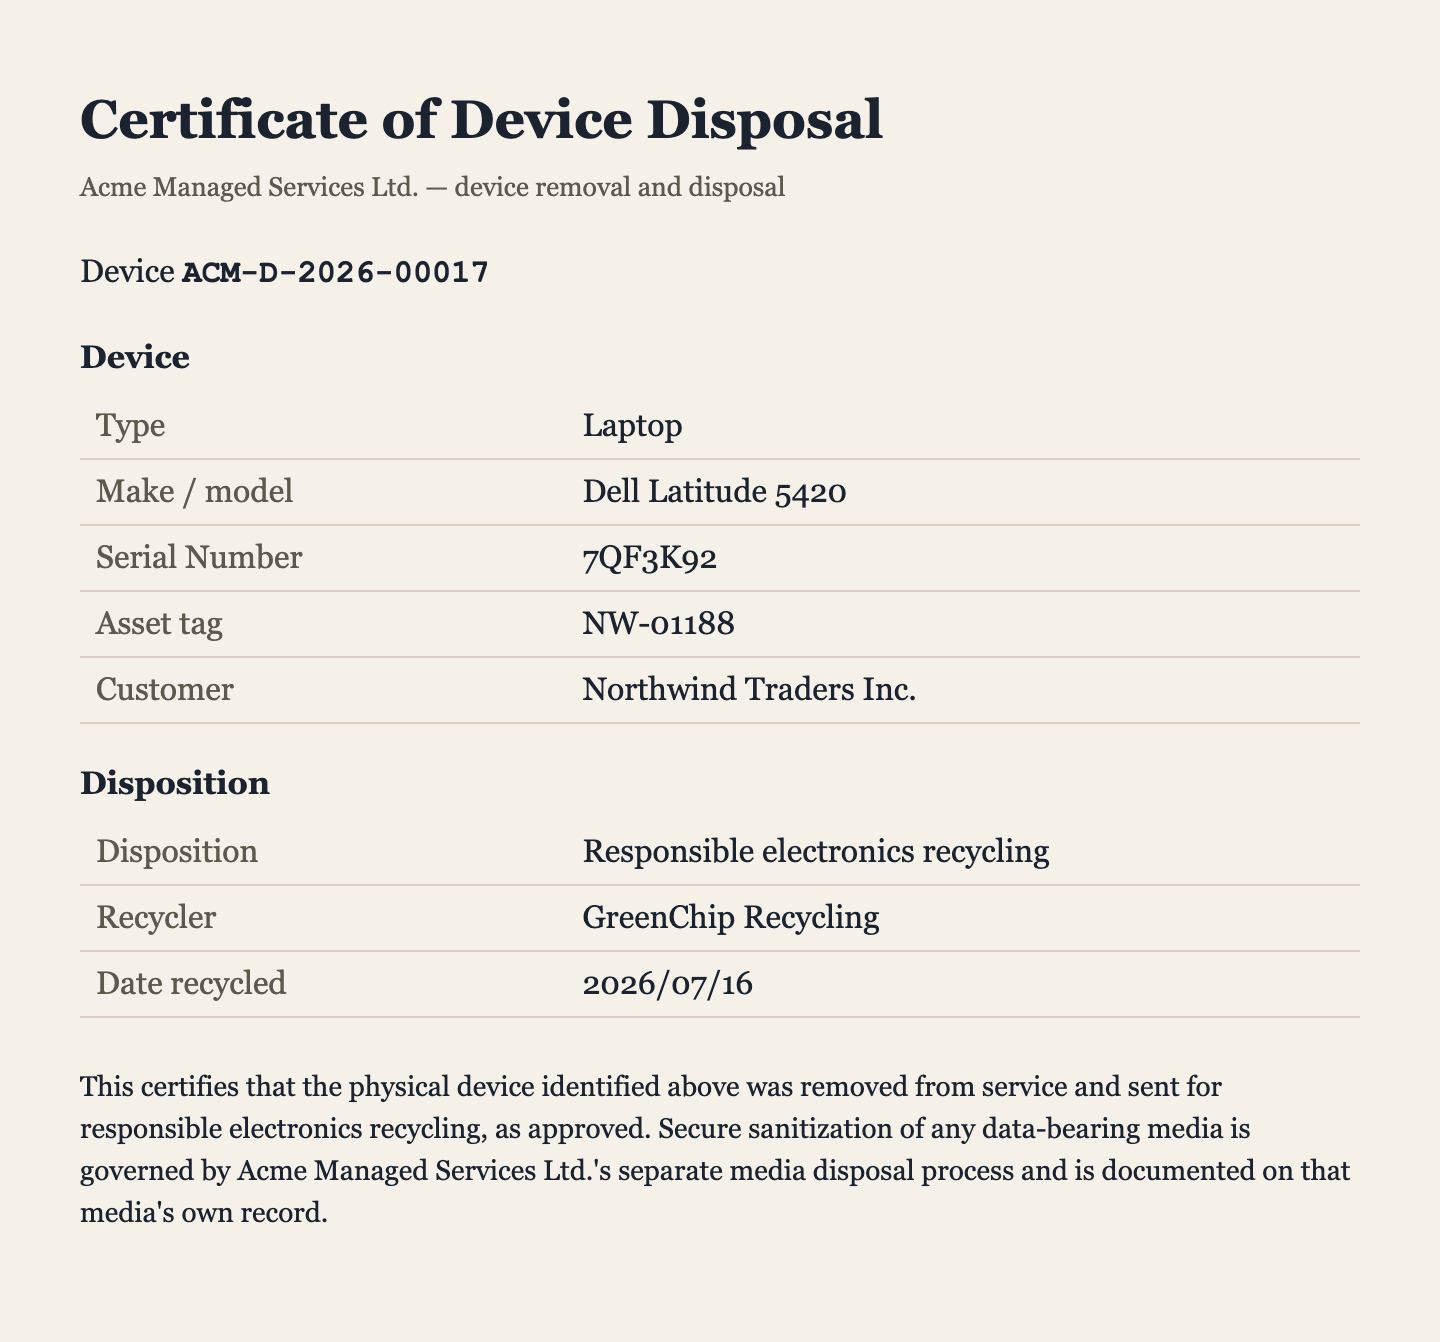
Document the device — laptop, desktop, or server — in the same intake as its drives. The customer signs once, and Custodyne issues a Certificate for every item: a Certificate of Destruction for each drive, and a Certificate of Device Disposal for the machine, recycled or returned to the customer. Each item gets its own QR label and its own place in the Chain of Custody.
Assets, batches, and the audit log
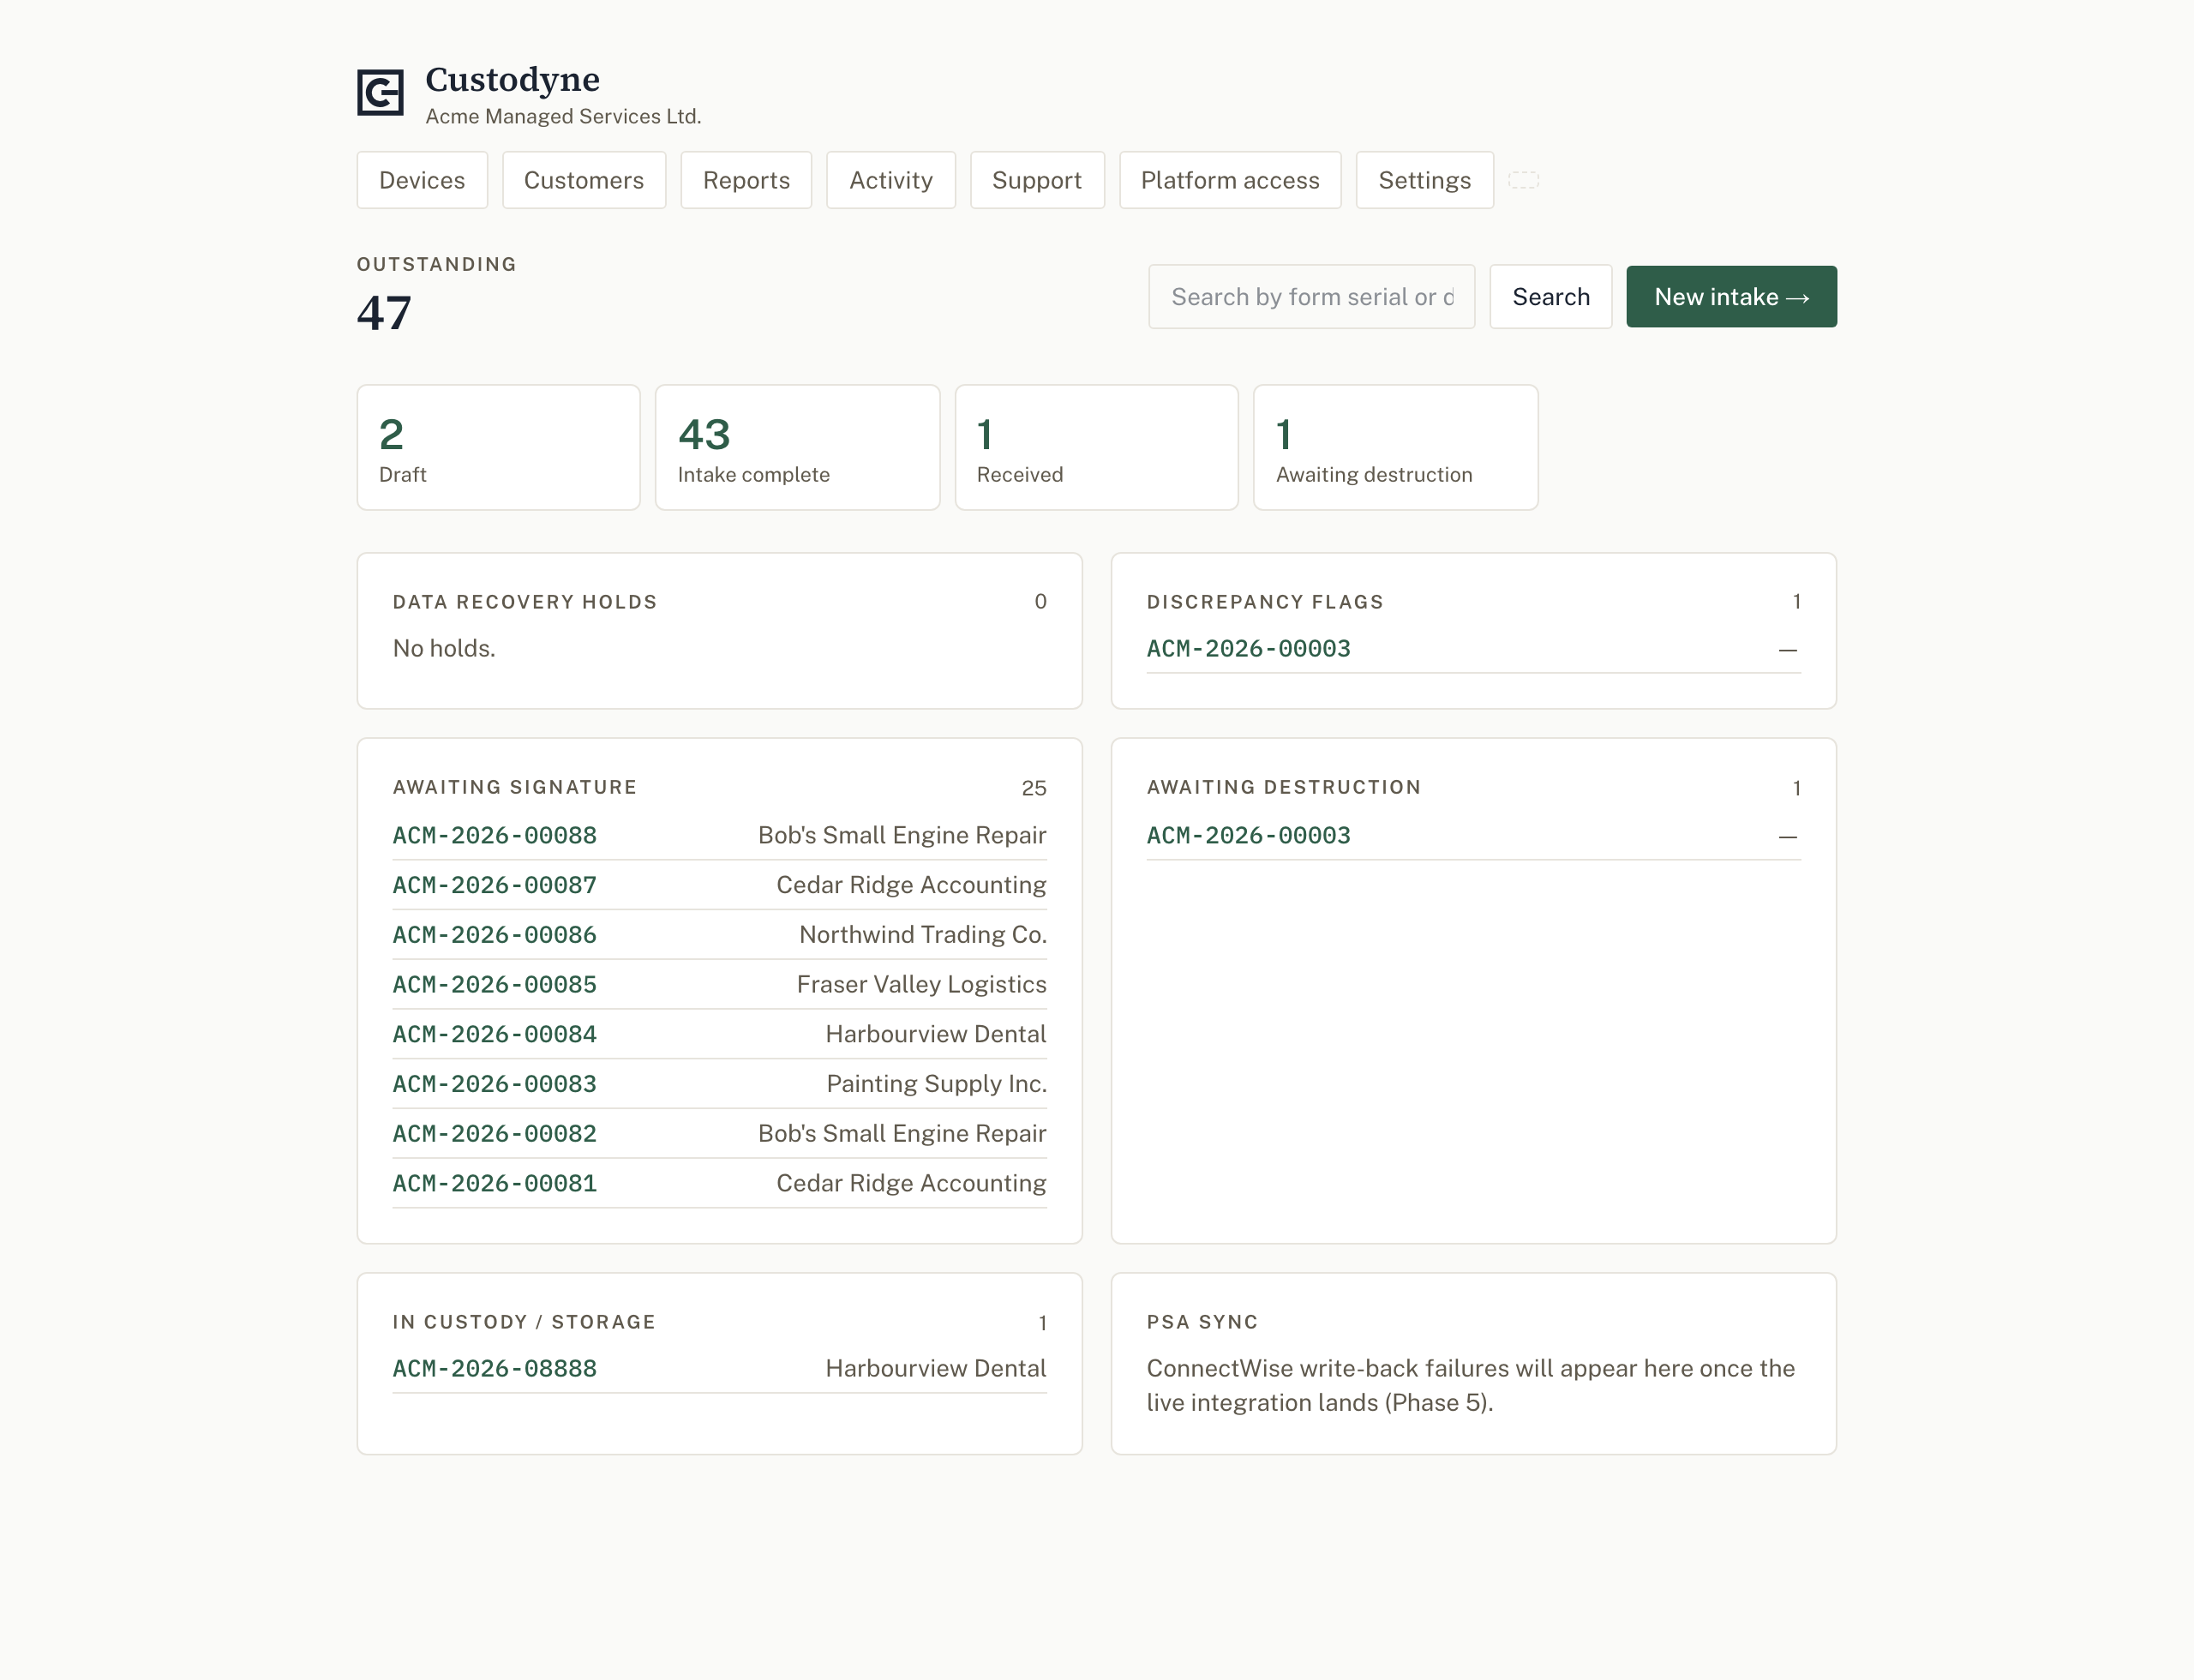
Office staff run the whole operation from one place: outstanding work by state, data-recovery holds, destruction batches, and a tamper-evident audit log — no spreadsheets, no gaps.
See it against your workflow
Beta participants run their real disposals in Custodyne and shape what it becomes before general release.
Join the Beta Program